- Cybertech Europe 2026 brought together international leaders to address emerging AI threats and digital resilience
- Industry leaders emphasized cyber survivability, innovation, and accountability
- Lithuania shows an example of strengthening national cyber defenses through NIS2 supervision, security operation centers, and cyber reserves
- Speakers called for stronger international cooperation, coordinated oversight, and convergent legislation to counter hybrid threats
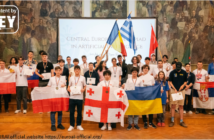
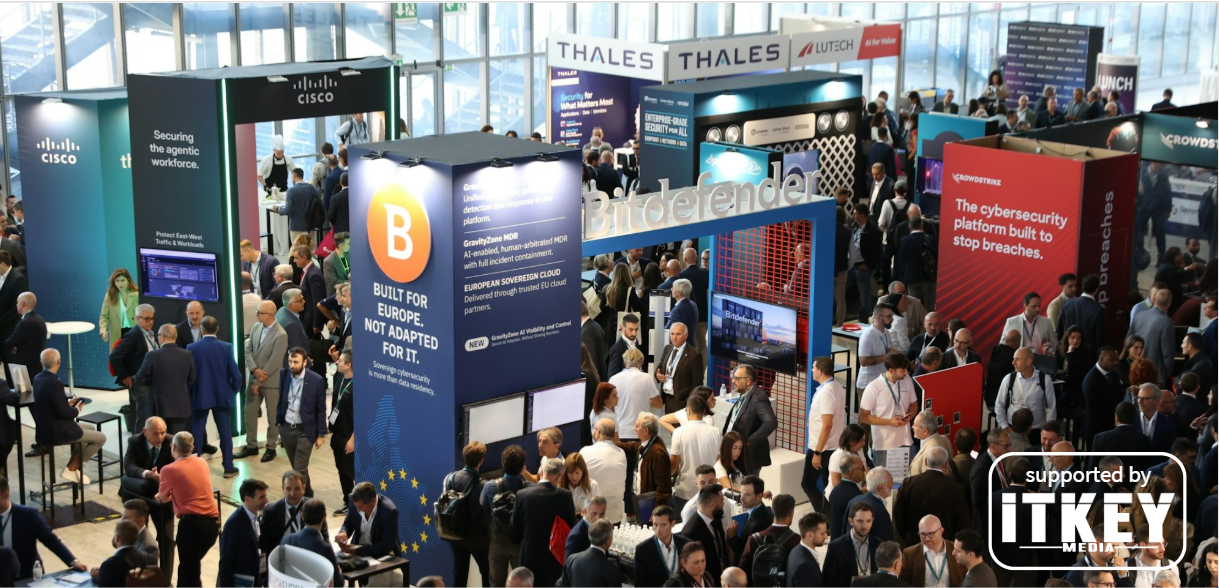
The 9th edition of Cybertech Europe, Europe’s leading platform for cybersecurity, technological innovation and digital resilience, took place on October 13–14th, 2026, at the La Nuvola Convention Center in Rome. Speakers from 19 countries, national cybersecurity leaders and CEOs addressed the new threats linked to AI, deepfakes and European digital resilience, while the Conference recorded a record number of attendees, with thousands of participants, reaffirming its position as one of Europe’s leading cybersecurity events.
David Byrne, Head of Information Superiority Unity at European Defense Agency
To share a glimpse of the event, ITKeyMedia spotlights the panel discussion Defense, Technology and Mission — Building Operational Resilience at Speed, involving the following speakers:
- Antanas Aleknavičius, Director of the Lithuanian National Cyber Security Centre of the Ministry of National Defense of Lithuania;
- Hon. Pedro Roque, VP of the Parliamentary Assembly of the Mediterranean;
- Aldo Sebastiani, SVP Global Cybersec Center, Cyber & Security Solutions Division at Leonardo;
- and David Byrne, Head of Information Superiority Unity at European Defense Agency, as the moderator.
Accelerating Innovation to Keep Pace with Emerging Threats
The discussion began with Mr Sebastiani sharing his opinion that what ensures proper resilience today is moving at a faster pace, due to the increasing use of AI by the adversary. According to his information, the time-to-exploit of a vulnerability collapsed from two years ten years ago to less than nine hours or even several minutes in certain cases. This is the pace at which the cyber security industry needs to deliver the technology today.
‘We consider innovation and security as two slides of the same coin to deliver operational resilience at speed and keep critical elements of infrastructure under pressure of attack conditions,’ he says.
With the military remaining the main source of security for citizens, Mr Aleknavičius shared how working with the military without being a military for 18 years helps him understand such significant nuances as the military never winning wars or battles on their own. It’s critical to invest in the citizens’ support for the military. When it comes to cyber security, the basics is informing the citizens about the main cyber threats and the inner workings of cyber security. AI is a great example of a ‘threat’ in the eyes of many citizens, but all they need is to understand better how it works and what to do about the possible threats that it may imply. Focusing on threats, meanwhile, forces these citizens to overlook the benefits of the mentioned AI. Naturally, forgetting about threats altogether and taking chances at all the promised benefits of AI is also not a solution. To balance these aspects, it’s important to talk about risk management, continuity, and the exact application of a technology to defend the country. Such talks are the most efficient with the involvement of the private and public sectors to encourage the citizens to trust and use the cyber security technologies.
Mr Roque, in turn, shared a parliamentary governmental perspective on how to strengthen existing cyber resilience systems. Parliamentary assemblies like PAM have a role of tackling ineffective regulation and legislation that slows down such innovation. Among other things that PAM is doing is preparing reports on the evolving AI risk landscape and the resilience of democratic systems.
‘Regarding the institutional capacity, effective control over risk requires supervisors with proper information, expertise, and authority. The regulation strategy is, instead of freezing innovation by regulating tools too late, legislation should focus on regulating outcomes to technological transparency accountably,’ he states.
Strengthening National Defenses and Critical Infrastructure
Antanas Aleknavičius, Director of the Lithuanian National Cyber Security Centre of the Ministry of National Defense of Lithuania
Mr Aleknavičius went on to specify the challenges and opportunities brought forth by AI. The first thing associated with the Lithuanian National Cyber Security Centre in this regard is supervision of how entities implement the NIS2 directive. As part of Lithuania’s MoD ecosystem, the Centre is also building and preparing critical infrastructure for what may come next. The goal is to have all the relevant players on board in an ecosystem where everybody knows their role if something should happen. The vision is a cyber reserve for defending critical infrastructure on the national level. This is an attempt to make a step further at reinforcing the Lithuanian public sector with an architecture of security operation centers: for each ministry to have at least one such center. The Lithuanian National Cyber Security Centre’s duty here is the prevention of possible coming threats.
At that, Mr Aleknavičius points out that while the technologies are new, the problems are mostly old. Specifically, while supervising the implementation of NIS2 and auditing entities, what’s revealed is lack of competencies, knowledge, and IT maintenance. The Centre’s mission is to exemplify and highlight the application and benefits of new technologies, including to tackle the shortage of intellectual resources instead of trying to hire a cyber security expert to solve all problems.
Mr Roque was asked about the measures to achieve a truly integrated approach to cyber resilience across the wider Euro-Mediterranean and Gulf areas, involving governments, industries, critical infrastructure operators, law enforcement, and academia to prevent large-scale attacks. The first most important condition that he named was clear legislation with binding standards for social media control and security measures, that would turn voluntary standards into actual defenses and overcome fragmentation.
‘Integration often fails when different entities hold isolated pieces of the puzzle instead of the whole picture,’ he comments.
In this situation, industry has to redefine security under the condition of not interfering inadvertently with the citizens’ freedom of action. As the main element for achieving this Mr Sebastiani named cyber survivability — the outcome-based resilience where essential elements remain available to accomplish missions even in degraded environments or under attack. Further, secure resilience means more than putting guardrails. Mission-critical sectors need to remain functional during the shift from a deterministic to non-deterministic approach. This allows industries the freedom to operate under extreme circumstances.
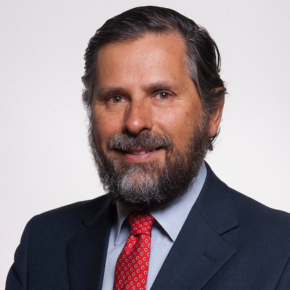
Hon. Pedro Roque, VP of the Parliamentary Assembly of the Mediterranean
If innovation advances more rapidly than expected, should public institutions adjust their processes or should industries adapt their expectations? Mr Roque favors the former over the latter. Framework agreements, modular and interoperable compliance, procurement should be designed to eliminate risk and not speed. At that, it’s up to industry to share a proportionate share of the burden: transparency of critical components, supporting obligations across the life of the system, and even the discipline of working up to the standards it did not write.
‘Speed in exchange for accountability is an honest bargain,’ he summarizes.
Interoperable Systems for a Networked Battlefield
In transition toward a multi-connected environment, a battlefield is becoming a network of networks, as Mr Byrne put it. The question is – How does the push for federated, interoperable systems redefine operational resilience at speed and what new vulnerabilities emerge at this speed? Mr Sebastiani believes that under the current geopolitically-contented conditions, more cooperation is needed just to begin approaching this complex track. Most apparently, cooperation provides the necessary technology. When we talk about operational resilience, this allows for going beyond a single capability and encompassing a distributed amount of capabilities, e.g. a federated constellation of satellites or a multi-agentic AI platform.
With the necessity for operational requirements to meet long-term planning, Mr Aleknavičius shared the opinion that member states should decisively invest in cooperation in the next five years — because technologies come and go.
‘We don’t know each other so well to help each other in case of need,’ he highlights.
Working together with all allies is the way to understand all the different ways in which we see cyber security. Especially since we already have a lot of excellent examples at hand.
A Shared Commitment to Meaningful Change
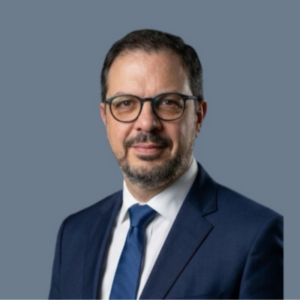
Aldo Sebastiani, SVP Global Cybersec Center, Cyber & Security Solutions Division at Leonardo
Finally, the moderator asked all three speakers what action could be the biggest catalyst to meaningful change in the approach to cyber resilience. Mr Sebastiani repeatedly underlined the importance of cyber survivability. This includes ensuring the secure continuous development of emerging technologies and thus secure control over these technologies and, consequently, catalyze true resilience.
Mr Aleknavičius reminded how for a long time cyber security proponents had to fight for attention from CEOs and national leaders. Today, cyber security has apparently grown into one of the top 3 priorities of every country, organization, and citizen. Relying so much on technologies, cyber resilience has become an apparent military-grade priority.
Mr Roque summarized that the universal catalyst should be the strategic cooperation and coordination, a unified commitment to legislative convergence, collective responsibility, and coordinated oversight of private actors. For instance, counter-intelligence interoperability should be embedded in parliaments’ legislation. Hybrid threats inadvertently cross borders, making cross-border cooperation critical.
Kostiantyn is a freelance writer from Crimea but based in Lviv. He loves writing about IT and high tech because those topics are always upbeat and he’s an inherent optimist!